

[2025] CS0-002 PDF Questions - Perfect Prospect To Go With 2Pass4sure Practice Exam
CompTIA CS0-002 Pdf Questions - Outstanding Practice To your Exam
The CS0-002 exam covers a wide range of topics, including threat and vulnerability management, network and host-based analysis, incident response, and compliance and regulations. It is an intermediate-level certification that builds upon the skills learned in the CompTIA Security+ certification and prepares professionals for more advanced cybersecurity roles.
CompTIA Cybersecurity Analyst (CySA+) certification exam, also known as CS0-002, is a globally recognized certification that validates the skills required to perform intermediate-level cybersecurity analysis. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification exam is designed for individuals who want to pursue a career in cybersecurity analysis, including security analysts, security operations center (SOC) analysts, and threat intelligence analysts. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification exam covers a variety of topics, including threat and vulnerability management, cybersecurity toolsets, security operations and monitoring, and incident response.
NEW QUESTION # 102
A security analyst is running a tool against an executable of an unknown source. The Input supplied by the tool to the executable program and the output from the executable are shown below: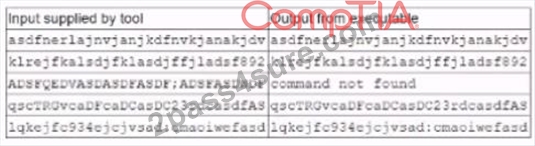
Which of the following should the analyst report after viewing this Information?
- A. The toot caused a buffer overflow in the executable's memory
- B. The executable attempted to execute a malicious command
- C. Input can be crafted to trigger an Infection attack in the executable
- D. A dynamic library that is needed by the executable a missing
Answer: A
Explanation:
A buffer overflow is a type of attack that exploits a vulnerability in an application or program that does not properly check the size or boundaries of an input. A buffer overflow occurs when an attacker supplies more data than the buffer can hold, causing the excess data to overwrite adjacent memory locations. This can result in unpredictable behavior, such as crashes, errors, data corruption, or execution of malicious code2 The tool that the analyst ran against the executable supplied an input that was too long for the buffer allocated by the executable. This caused a buffer overflow in the executable's memory, as indicated by the error message "Segmentation fault (core dumped)".
NEW QUESTION # 103
A network attack that is exploiting a vulnerability in the SNMP is detected.
Which of the following should the cybersecurity analyst do FIRST?
- A. Apply the required patches to remediate the vulnerability.
- B. Disable all privileged user accounts on the network.
- C. Escalate the incident to senior management for guidance.
- D. Temporarily block the attacking IP address.
Answer: A
Explanation:
Reference:
https://beyondsecurity.com/scan-pentest-network-vulnerabilities-snmp-protocol-version- detection.html
NEW QUESTION # 104
A company's application development has been outsourced to a third-party development team. Based on the SLA.
The development team must follow industry best practices for secure coding. Which of the following is the BEST way to verify this agreement?
- A. Application fuzzing
- B. Input validation
- C. User acceptance testing
- D. Stress testing
- E. Security regression testing
Answer: C
NEW QUESTION # 105
A security analyst reviews SIEM logs and discovers the following error event:
Which of the following environments does the analyst need to examine to continue troubleshooting the event?
- A. WAF appliance
- B. SQL server
- C. Proxy server
- D. DNS server
- E. Windows domain controller
Answer: D
NEW QUESTION # 106
A consultant evaluating multiple threat intelligence leads to assess potential risks for a client. Which of the following is the BEST approach for the consultant to consider when modeling the client's attack surface?
- A. Ask for external scans from industry peers, look at the open ports, and compare Information with the client.
- B. Look at attacks against similar industry peers and assess the probability of the same attacks happening.
- C. Meet with the senior management team to determine if funding is available for recommended solutions.
- D. Discuss potential tools the client can purchase lo reduce the livelihood of an attack.
Answer: B
NEW QUESTION # 107
Industry partners from critical infrastructure organizations were victims of attacks on their SCADA devices.
The attacker was able to gain access to the SCADA by logging in to an account with weak credentials. Which of the following identity and access management solutions would help to mitigate this risk?
- A. Role-based access control
- B. Manual access reviews
- C. Endpoint detection and response
- D. Multifactor authentication
Answer: A
Explanation:
Explanation
RBAC helps organizations manage access to critical infrastructure networks by assigning access based on roles. This allows organizations to control who can access specific resources and helps eliminate weak credentials that attackers could exploit. Manual reviews and endpoint detection and response can also help to mitigate risk, but role based access control is the best solution for this scenario.
NEW QUESTION # 108
A cyber-incident response analyst is investigating a suspected cryptocurrency miner on a company's server.
Which of the following is the FIRST step the analyst should take?
- A. Create a full disk image of the server's hard drive to look for the file containing the malware.
- B. Take a memory snapshot of the machine to capture volatile information stored in memory.
- C. Run a manual antivirus scan on the machine to look for known malicious software.
- D. Start packet capturing to look for traffic that could be indicative of command and control from the miner.
Answer: D
NEW QUESTION # 109
A Chief Information Security Officer (CISO) is concerned the development team,
which consists of contractors, has too much access to customer dat
Developers use personal workstations, giving the company little to no visibility into the development activities.
Which of the following would be BEST to implement to alleviate the CISO's concern?
- A. NDA
- B. Test data
- C. DLP
- D. Encryption
Answer: A
NEW QUESTION # 110
An analyst must review a new cloud-based SIEM solution. Which of the following should the analyst do FIRST prior to discussing the company's needs?
- A. Check industry news feeds for product reviews.
- B. Perform a vulnerability scan against a test instance.
- C. Download the product security white paper.
- D. Ensure a current non-disclosure agreement is on file
Answer: D
NEW QUESTION # 111
A consultant evaluating multiple threat intelligence leads to assess potential risks for a client. Which of the following is the BEST approach for the consultant to consider when modeling the client's attack surface?
- A. Ask for external scans from industry peers, look at the open ports, and compare Information with the client.
- B. Look at attacks against similar industry peers and assess the probability of the same attacks happening.
- C. Meet with the senior management team to determine if funding is available for recommended solutions.
- D. Discuss potential tools the client can purchase lo reduce the livelihood of an attack.
Answer: B
Explanation:
A good approach for modeling the client's attack surface is to look at attacks against similar industry peers and assess the probability of the same attacks happening. This can help the consultant to identify the most relevant and likely threats for the client based on their industry sector, size, location, and other factors. This can also help the consultant to prioritize the most critical risks and recommend appropriate mitigation strategies. Asking for external scans from industry peers (A) may not be feasible or reliable, as industry peers may not share their scan results or have different security configurations and vulnerabilities than the client. Discussing potential tools the client can purchase (B) may not be effective, as tools alone cannot reduce the likelihood of an attack without proper implementation and management. Meeting with senior management team (D) may not be helpful, as funding is not directly related to modeling the attack surface and may depend on other factors such as budget constraints and risk appetite.
NEW QUESTION # 112
While conoXicting a cloud assessment, a security analyst performs a Prowler scan, which generates the following within the report: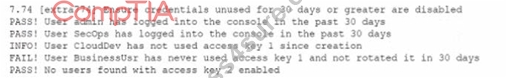
Based on the Prowler report, which of the following is the BEST recommendation?
- A. Delete access key 2.
- B. Delete access key 1.
- C. Delete BusinessUsr access key 1.
- D. Delete Cloud Dev access key 1
Answer: A
NEW QUESTION # 113
An ATM in a building lobby has been compromised. A security technician has been advised that the ATM must be forensically analyzed by multiple technicians. Which of the following items in a forensic tool kit would likely be used FIRST? (Select TWO).
- A. Write blockers
- B. Drive imager
- C. Drive adapters
- D. Chain of custody form
- E. Crime tape
- F. Hashing utilities
Answer: A,D
NEW QUESTION # 114
A security analyst is analyzing the following output from the Spider tab of OWASP ZAP after a vulnerability scan was completed: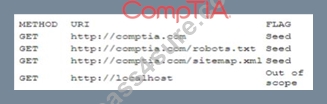
Which of the following options can the analyst conclude based on the provided output?
- A. The scanner executed a crawl process to discover pages to be assessed
- B. The scanning job did not successfully complete due to an out of scope error
- C. The scanning vendor used robots to make the scanning job faster
- D. The scanning job was successfully completed, and no vulnerabilities were detected
Answer: A
Explanation:
The output shows the result of using OWASP ZAP's Spider tab after a vulnerability scan was completed. The Spider tab allows users to crawl web applications and discover pages and resources that can be assessed for vulnerabilities. The output shows that the scanner discovered various pages under different directories, such as /admin/, /blog/, /contact/, etc., as well as some parameters and forms that can be used for testing inputs and outputs. Reference: CompTIA Cybersecurity Analyst (CySA+) Certification Exam Objectives (CS0-002), page 9; https://www.zaproxy.org/docs/desktop/start/features/spider/
NEW QUESTION # 115
A company's Chief Information Security Officer (CISO) is concerned about the integrity of some highly confidential files. Any changes to these files must be tied back to a specific authorized user's activity session. Which of the following is the BEST technique to address the CISO's concerns?
- A. Configure DLP to reject all changes to the files without pre-authorization. Monitor the files for unauthorized changes.
- B. Use Wireshark to scan all traffic to and from the directory. Monitor the files for unauthorized changes.
- C. Regularly use SHA-256 to hash the directory containing the sensitive information. Monitor the files for unauthorized changes.
- D. Place a legal hold on the files. Require authorized users to abide by a strict time context access policy.
Monitor the files for unauthorized changes.
Answer: A,D
NEW QUESTION # 116
Given the following code: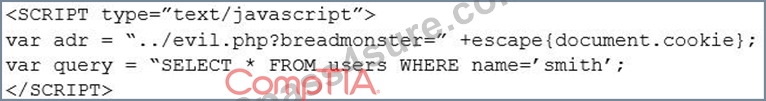
Which of the following types of attacks is occurring in the example above?
- A. Privilege escalation
- B. SQL injection
- C. MITM
- D. Session hijacking
- E. XSS
Answer: B
NEW QUESTION # 117
While investigating an incident in a company's SIEM console, a security analyst found hundreds of failed SSH login attempts, which all occurred in rapid succession. The failed attempts were followed by a successful login on the root user Company policy allows systems administrators to manage their systems only from the company's internal network using their assigned corporate logins. Which of the following are the BEST actions the analyst can take to stop any further compromise? (Select TWO).
- A. Add a rule on the perimeter firewall to block the source IP address.
- B. Reset the passwords for all accounts on the affected system.
- C. Configure /etc/sshd_config to deny root logins and restart the SSHD service.
- D. Configure /etc/passwd to deny root logins and restart the SSHD service.
- E. Add a rule on the affected system to block access to port TCP/22.
- F. Add a rule on the network IPS to block SSH user sessions
Answer: A,D
NEW QUESTION # 118
A security analyst reviews the following aggregated output from an Nmap scan and the border firewall ACL: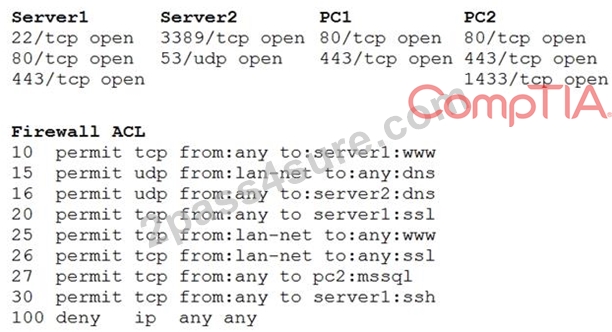
Which of the following should the analyst reconfigure to BEST reduce organizational risk while maintaining current functionality?
- A. PC1
- B. Server2
- C. Server1
- D. PC2
- E. Firewall
Answer: D
NEW QUESTION # 119
A cybersecurity analyst has access to several threat feeds and wants to organize them while simultaneously comparing intelligence against network traffic.
Which of the following would BEST accomplish this goal?
- A. Continuous integration and deployment
- B. Information sharing and analysis
- C. Static and dynamic analysis
- D. Automation and orchestration
Answer: C
NEW QUESTION # 120
A company experienced a security compromise due to the inappropriate disposal of one of its hardware appliances. Sensitive information stored on the hardware appliance was not removed prior to disposal. Which of the following is the BEST manner in which to dispose of the hardware appliance?
- A. Ensure the hardware appliance has the ability to encrypt the data before disposing of it.
- B. Establish guidelines for the handling of sensitive information.
- C. Dispose of all hardware appliances securely, thoroughly, and in compliance with company policies.
- D. Return the hardware appliance to the vendor, as the vendor is responsible for disposal.
Answer: C
Explanation:
Secure and thorough disposal can involve deleting or wiping all data from the hardware appliances, physically destroying or shredding them, or recycling them through certified vendors or programs. Compliance with company policies can help to ensure that the disposal follows the best practices and standards for data protection and environmental responsibility .
NEW QUESTION # 121
Creating an isolated environment in order to test and observe the behavior of unknown software is also known as:
- A. sandboxing
- B. sniffing
- C. hardening
- D. hashing
Answer: A
NEW QUESTION # 122
A security analyst is evaluating two vulnerability management tools for possible use in an organization. The analyst set up each of the tools according to the respective vendor's instructions and generated a report of vulnerabilities that ran against the same target server.
Tool A reported the following: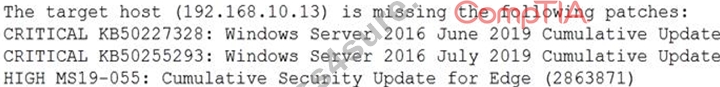
Tool B reported the following:
Which of the following BEST describes the method used by each tool? (Choose two.)
- A. Tool B utilized machine learning technology.
- B. Tool B is unauthenticated.
- C. Tool B is agent based.
- D. Tool A is agent based.
- E. Tool A is unauthenticated.
- F. Tool A used fuzzing logic to test vulnerabilities.
Answer: C,E
NEW QUESTION # 123
A security analyst is reviewing the following log from an email security service.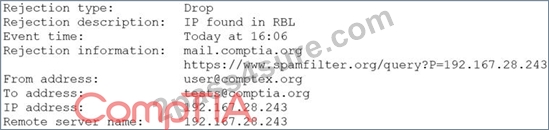
Which of the following BEST describes the reason why the email was blocked?
- A. The To address is invalid.
- B. The IP address was blacklisted.
- C. The IP address and the remote server name are the same.
- D. The email originated from the www.spamfilter.org URL.
- E. The From address is invalid.
Answer: C
NEW QUESTION # 124
A security analyst is auditing firewall rules with the goal of scanning some known ports to check the firewall's behavior and responses. The analyst executes the following commands: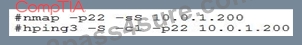
The analyst then compares the following results for port 22:
nmap returns "Closed"
hping3 returns "flags=RA"
Which of the following BEST describes the firewall rule?
- A. LOG --log-tcp-sequence
- B. DNAT --to-destination 1.1.1.1:3000
- C. REJECT with --tcp-reset
- D. DROP
Answer: D
NEW QUESTION # 125
An analyst determines a security incident has occurred Which of the following is the most appropnate NEXT step in an incident response plan?
- A. Consult the communications plan
- B. Consult the data classification process
- C. Consult the malware analysis process
- D. Consult the disaster recovery plan
Answer: A
Explanation:
A communications plan is a document that outlines who should be notified and how during an incident response. It can also specify the roles and responsibilities of the incident response team members, the escalation procedures, and the communication channels. Consulting the communications plan is the most appropriate next step in an incident response plan after determining a security incident has occurred. Consulting the malware analysis process, the disaster recovery plan, or the data classification process may be relevant at later stages of the incident response, but not as the next step. Reference: https://www.sans.org/reading-room/whitepapers/incident/incident-handlers-handbook-33901
NEW QUESTION # 126
......
Online Questions - Outstanding Practice To your CS0-002 Exam: https://www.2pass4sure.com/CompTIA-CySA/CS0-002-actual-exam-braindumps.html
Practice To CS0-002 - 2Pass4sure Remarkable Practice On your CompTIA Cybersecurity Analyst (CySA+) Certification Exam Exam: https://drive.google.com/open?id=1VPB8Kfhk2rvE8ke_3o9WIHvp9FDDQNFL