

300-710 Actual Questions Answers Pass With Real 300-710 Exam Dumps
300-710 Dumps Prepare Your Exam With 423 Questions
Cisco 300-710 exam is designed for professionals who are responsible for implementing and managing security solutions using Cisco Firepower technology. 300-710 exam covers a range of topics related to network security, such as network access control, threat defense, and malware protection. It also includes hands-on lab exercises to test the candidate's ability to configure and troubleshoot Firepower devices and software.
NEW QUESTION # 221
Which action should be taken after editing an object that is used inside an access control policy?
- A. Refresh the Cisco FMC GUI for the access control policy.
- B. Create another rule using a different object name.
- C. Delete the existing object in use.
- D. Redeploy the updated configuration.
Answer: D
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/firepower/630/configuration/guide/fpmc-config- guide-v63/reusable_objects.html
NEW QUESTION # 222
How does Cisco Secure Cloud Analytics handle information about network traffic?
- A. It performs a behavioral analysis on events and network flow data.
- B. It performs a heuristic analysis on events and network flow data.
- C. It forwards the information to other devices without storing it.
- D. It stores the information in a database without any analysis.
Answer: A
Explanation:
Cisco Secure Cloud Analytics (formerly Stealthwatch Cloud) uses behavioral analysis to monitor events and network flow data. It builds a baseline of normal network behavior and then detects anomalies, such as data exfiltration or lateral movement, indicating potential threats.
NEW QUESTION # 223
Network users are experiencing Intermittent issues with internet access. An engineer ident med mat the issue Is being caused by NAT exhaustion. How must the engineer change the dynamic NAT configuration to provide internet access for more users without running out of resources?
- A. Define an additional static NAT for the network object in use.
- B. Add an identity NAT rule to handle the overflow of users.
- C. Convert the dynamic auto NAT rule to dynamic manual NAT.
- D. Configure fallthrough to interface PAT on 'he Advanced tab.
Answer: D
Explanation:
Fallthrough to interface PAT is a feature that allows the dynamic NAT configuration to use the interface IP address as a last resort when the NAT pool is exhausted. This way, more users can access the internet without running out of resources. To enable this feature, the engineer must check the Enable PAT Fallback check box on the Advanced tab of the NAT rule editor1
NEW QUESTION # 224
An engineer is setting up a remote access VPN on a Cisco FTD device and wants to define which traffic gets sent over the VPN tunnel. Which named object type in Cisco FMC must be used to accomplish this task?
- A. crypto map
- B. split tunnel
- C. route map
- D. access list
Answer: D
Explanation:
You can specify the access list in Objects that needs to be used for interesting traffic.
NEW QUESTION # 225 
Refer to the exhibit. An engineer must import three network objects into the Cisco Secure Firewall Management Center by using a CSV file. Which header must be configured in the CSV file to accomplish the task?
- A. NAME;DESCRIPTION; TYPE;VALUE;DN;
- B. Name; Description; Type;Value;DN;
- C. Name; Description; Type;Value;Lookup;
- D. NAME;DESCRIPTION;TYPE;VALUE;LOOKUP;
Answer: D
NEW QUESTION # 226
A Cisco FTD device is running in transparent firewall mode with a VTEP bridge group member ingress interface What must be considered by an engineer tasked with specifying a destination MAC address for a packet trace?
- A. The destination MAC address is optional if a VLAN ID value is entered
- B. Only the UDP packet type is supported
- C. The output format option for the packet logs unavailable
- D. The VLAN ID and destination MAC address are optional
Answer: A
NEW QUESTION # 227
An administrator is configuring a new report template off. of a saved search within Cisco Secure Firewall Management Centre. The goal is to use the malware analysis report template, but use a different type saved search as the basis. The report is not working. What must be considered when configuring this report template?
- A. Saved searches are available freely for all report templates within the same domain.
- B. Saved searches from a different report template must be used.
- C. Saved searches can be used for the same report template only
- D. Saved searches must be renamed before using for different report template.
Answer: C
Explanation:
When configuring a new report template based on a saved search in Cisco Secure Firewall Management Center (FMC), it is important to note that saved searches are specific to the report template they were created with. Saved searches cannot be freely used across different report templates.
To use a different type of saved search, you must ensure that it aligns with the specific report template being used.
This restriction ensures that the saved search parameters match the report's data requirements.
NEW QUESTION # 228
After deploying a network-monitoring tool to manage and monitor networking devices in your organization, you realize that you need to manually upload an MIB for the Cisco FMC. In which folder should you upload the MIB file?
- A. /etc/sf/DCMIB.ALERT
- B. /etc/sf/DCEALERT.MIB
- C. system/etc/DCEALERT.MIB
- D. /sf/etc/DCEALERT.MIB
Answer: B
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/firesight/541/firepower-module-user-guide/asa- firepower-module-user-guide-v541/Intrusion-External-Responses.pdf
NEW QUESTION # 229
An engineer is deploying failover capabilities for a pair of Cisco Secure Firewall devices. The core switch keeps the MAC address of the previously active unit in the ARP table. Which action must the engineer take to minimize downtime and ensure that network users keep access to the internet after a Cisco Secure Firewall failover?
- A. Use a virtual MAC address on both units
- B. Run a script to send gratuitous ARP after a failover.
- C. Add the MAC address to the switch ARP table.
- D. Set the same MAC address on both units.
Answer: A
NEW QUESTION # 230
An administrator is setting up Cisco Firepower to send data to the Cisco Stealthwatch appliances. The NetFlow_Set_Parameters object is already created, but NetFlow is not being sent to the flow collector. What must be done to prevent this from occurring?
- A. Add the NetFlow_Send_Destination object to the configuration
- B. Add the NetFlow_Add_Destination object to the configuration
- C. Create a service identifier to enable the NetFlow service
- D. Create a Security Intelligence object to send the data to Cisco Stealthwatch
Answer: B
Explanation:
Cisco Firepower uses FlexConfig objects to send NetFlow data. Here's the key point:
NetFlow_Set_Parameters object: Defines the parameters of the NetFlow data being exported (e.g., version, sampling rate).
NetFlow_Add_Destination object: Specifies the IP address and port of the flow collector (in this case, your Cisco Stealthwatch appliance) where the NetFlow data should be sent.
NEW QUESTION # 231
A network administrator notices that SI events are not being updated The Cisco FTD device is unable to load all of the SI event entries and traffic is not being blocked as expected. What must be done to correct this issue?
- A. Manually update the SI event entries to that the appropriate traffic is blocked
- B. Replace the affected devices with devices that provide more memory
- C. Redeploy configurations to affected devices so that additional memory is allocated to the SI module
- D. Restart the affected devices in order to reset the configurations
Answer: C
NEW QUESTION # 232
An engineer is configuring URL filtering for a Cisco FTD device in Cisco FMC. Users must receive a warning when they access http:/'www.Dac'additstte.corn with the option of continuing to the website if they choose to. No other websites should be blacked. Which two actions must the engineer lake to meet these requirements? (Choose two.)
- A. On the HTTP Responses tab of the access control policy editor, set the Block Response Page to Custom.
- B. Configure an access control rule that matches the Adult URL category and se: the action to interactive Block.
- C. Configure the default action for the access control policy to Interactive Block.
- D. Configure an access control rule that matches an URL object for http://www.badaduitslte.com; and set the action to interactive Block.
- E. On the HTTP Responses tab of the access control policy editor, sot the Interactive Block Response Page to system-provided.
Answer: D,E
Explanation:
To configure URL filtering for a Cisco FTD device in Cisco FMC, and to meet the requirements of the question, the engineer must do the following:
* On the HTTP Responses tab of the access control policy editor, set the Interactive Block Response Page to system-provided. This will enable the system to display a warning page to the users when they try to access a blocked URL, and give them the option to continue or cancel. The system-provided page is a default page that contains a generic message and a logo1.
* Configure
an access control rule that matches an URL object for http://www.badadultsite.com; and set the action to Interactive Block. This will apply the interactive block action to the specific URL that is defined in the URL object.
The interactive block action will trigger the interactive block response page that was configured in the previous step1.
The other options are incorrect because:
* On the HTTP Responses tab of the access control policy editor, setting the Block Response Page to Custom will not affect the interactive block action. The block response page is used when the action is set to Block, not Interactive Block1.
* Configuring the default action for the access control policy to Interactive Block will apply the interactive block action to all URLs that are not matched by any access control rule. This will not meet the requirement of blocking no other websites1.
* Configuring an access control rule that matches the Adult URL category and sets the action to Interactive Block will apply the interactive block action to all URLs that belong to the Adult category.
This
will not meet the requirement of blocking only http://www.badadultsite.com
1.
NEW QUESTION # 233
An engineer is configuring a second Cisco FMC as a standby device but is unable to register with the active unit.
What is causing this issue?
- A. The licensing purchased does not include high availability
- B. There is only 10 Mbps of bandwidth between the two devices.
- C. The code versions running on the Cisco FMC devices are different
- D. The primary FMC currently has devices connected to it.
Answer: C
Explanation:
FMC High Availability. High Availability is available on physical Firepower Management Center appliances (and FMCv since 6.7. 0).
Before configuring FMC HA make sure that:
* Hardware is identical (no mix and match between virtual and/or physical form factors)
* Software release is identical on both FMCs
* There are no sensors registered to the secondary FMC
https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config- guide-v62/firepower_management_center_high_availability.html
NEW QUESTION # 234
An administrator is creating interface objects to better segment their network but is having trouble adding interfaces to the objects. What is the reason for this failure?
- A. The interfaces are being used for NAT for multiple networks.
- B. The administrator is adding interfaces of multiple types.
- C. The interfaces belong to multiple interface groups.
- D. The administrator is adding an interface that is in multiple zones.
Answer: C
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config-guide-v62/reusa
"All interfaces in an interface object must be of the same type: all inline, passive, switched, routed, or ASA FirePOWER. After you create an interface object, you cannot change the type of interfaces it contains."
NEW QUESTION # 235
Which license type is required on Cisco ISE to integrate with Cisco FMC pxGrid?
- A. apex
- B. plus
- C. mobility
- D. base
Answer: B
Explanation:
The Cisco Identity Services Engine (ISE) uses the Platform Exchange Grid (pxGrid) to integrate with other security products, such as the Cisco Firepower Management Center (FMC). To use pxGrid, a Plus license is required on Cisco ISE. The Plus license provides advanced network access control and security features, including integration with third-party products via pxGrid.
https://www.cisco.com/c/en/us/products/collateral/security/identity-services-engine/ise-licensing- guide-og.html#3CiscoISELicenses
NEW QUESTION # 236
A network administrator registered a new FTD to an existing FMC. The administrator cannot place the FTD in transparent mode. Which action enables transparent mode?
- A. Assign an IP address to two physical interfaces.
- B. Obtain an FTD model that supports transparent mode.
- C. Add a Bridge Group Interface to the FTD before transparent mode is configured.
- D. Deregister the FTD device from FMC and configure transparent mode via the CLI.
Answer: D
NEW QUESTION # 237
An engineer must integrate a thud-party security Intelligence teed with Cisco Secure Firewall Management Center. Secure Firewall Management Center is running Version 6.2 3 and has 8 GB of memory. Which two actions must be taken to implement Throat Intelligence Director? (Choose two.)
- A. Add the URL of the TAXII server.
- B. Add 7 GB of memory.
- C. Upgrade to version 6.6.
- D. Add a TAXII server
- E. Enable REST API access.
Answer: A,C
Explanation:
To integrate a third-party security intelligence feed with Cisco Secure Firewall Management Center (FMC) using Threat Intelligence Director (TID), the following actions are necessary:
* Upgrade to version 6.6: The FMC must be running at least version 6.6 to support Threat Intelligence Director. Version 6.2.3 does not support the necessary features for this integration.
* Add the URL of the TAXII server: Threat Intelligence Director uses TAXII (Trusted Automated eXchange of Indicator Information) to pull threat intelligence data from third-party sources. The URL of the TAXII server must be added to the TID configuration in FMC.
Steps:
* Upgrade FMC to version 6.6 or later.
* In FMC, navigate to Integration > Threat Intelligence Director.
* Add a new TAXII server by entering the URL of the TAXII server.
These actions enable the integration of third-party threat intelligence feeds, enhancing the security capabilities of the FMC.
References: Cisco Secure Firewall Management Center Administrator Guide, Chapter on Threat Intelligence Director.
NEW QUESTION # 238
An engineer is configuring a Cisco Secure Firewall Threat Defense device to operate in transparent mode between two switch stacks. VLAN 10 is used for in-band management on both switch stacks. Which two actions are required on the device to inspect traffic between the switch stacks without interrupting network traffic? (Choose two.)
- A. Configure at least one bridge group.
- B. Add separate routes for data and management traffic.
- C. Exempt BPDUs from advanced inspection.
- D. Configure a BVI interface for VLAN 10.
- E. Set the MTU to 9198 on all interfaces to support jumbo frames.
Answer: A,C
Explanation:
Transparent firewall mode forwards traffic at Layer 2, so the participating physical interfaces must be assigned to at least one bridge group. This allows the device to inspect traffic while remaining logically transparent to the connected switch stacks. Bridge Protocol Data Units should also be exempted from advanced inspection. BPDUs are essential for spanning-tree operation, and delaying or blocking them during inspection restarts can produce topology instability or an interruption. A BVI provides Layer 3 addressing for device-originated traffic or management but is not inherently required merely to inspect transit traffic. Jumbo- frame configuration is unnecessary unless the network explicitly uses jumbo frames, and separate data and management routes do not establish transparent forwarding. Cisco specifically recommends using an EtherType ACL to trust BPDUs on each bridge-group member interface. Cisco transparent firewall configuration
NEW QUESTION # 239
Drag and drop the steps to restore an automatic device registration failure on the standby Cisco FMC from the left into the correct order on the right. Not all options are used.
Answer:
Explanation: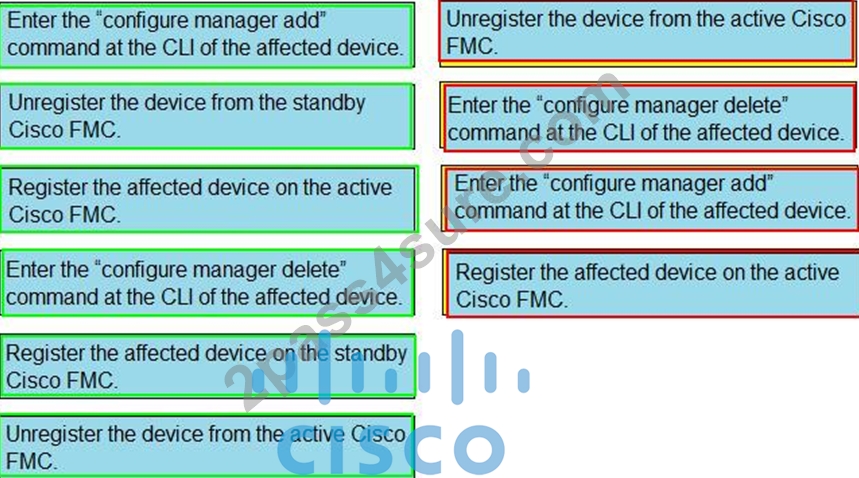
NEW QUESTION # 240
Refer to the exhibit.
And engineer is analyzing the Attacks Risk Report and finds that there are over 300 instances of new operating systems being seen on the network How is the Firepower configuration updated to protect these new operating systems?
- A. Cisco Firepower gives recommendations to update the policies.
- B. Cisco Firepower automatically updates the policies.
- C. The administrator requests a Remediation Recommendation Report from Cisco Firepower
- D. The administrator manually updates the policies.
Answer: A
Explanation:
Ref:
https://www.cisco.com/c/en/us/td/docs/security/firepower/60/configuration/guide/fpmc-config-guide-v60/Tailori
NEW QUESTION # 241
Refer to the exhibit.
An engineer generates troubleshooting files in Cisco Secure Firewall Management Center (FMC). A successfully completed task Is removed before the files are downloaded. Which two actions must be taken to determine the filename and obtain the generated troubleshooting files without regenerating them? (Choose two.)
- A. Use an FTP client Hi expert mode on Secure FMC lo upload the files to the FTP server.
- B. Connect to CU on the FTD67 and FTD66 devices and copy the tiles from flash to the PIP server.
- C. Go to the same screen as shown in the exhibit, click Advanced Troubleshooting, enter the rile name, and then start the download
- D. Click System Monitoring, men Audit to determine the correct filename from the line containing the Generate Troubleshooting Files string.
- E. Go to expert mode on Secure FMC. list the contents of/Var/common, and determine the correct filename from the output
Answer: D,E
Explanation:
If a task to generate troubleshooting files in Cisco Secure Firewall Management Center (FMC) is completed successfully but removed before the files are downloaded, the following steps can be taken to determine the filename and obtain the generated troubleshooting files without regenerating them:
* Go to expert mode on Secure FMC:
* Access expert mode on the FMC via SSH or the console.
* List the contents of the directory /var/common to locate the generated troubleshooting files. Use the command ls /var/common.
* Use the System Monitoring Audit logs:
* In FMC, navigate to System > Monitoring > Audit.
* Find the line containing the "Generate Troubleshooting Files" string to determine the correct filename.
These actions help identify and retrieve the generated troubleshooting files without the need to regenerate them, saving time and resources.
References: Cisco Secure Firewall Management Center Administrator Guide, Chapter on Troubleshooting and File Management.
NEW QUESTION # 242
......
New 300-710 Dumps - Real Cisco Exam Questions: https://www.2pass4sure.com/CCNPSecurity/300-710-actual-exam-braindumps.html
Dependable 300-710 Exam Dumps to Become Cisco Certified: https://drive.google.com/open?id=1wy5I4_X0E00ct7tOsSwSUUhjInqSmDKF