

Exam Questions Answers Braindumps CS0-002 Exam Dumps PDF Questions
Download Free CompTIA CS0-002 Real Exam Questions
CompTIA CS0-002 Exam Syllabus Topics:
| Topic | Details |
|---|---|
Threat and Vulnerability Management - 22% | |
| Explain the importance of threat data and intelligence. | 1. Intelligence sources
2. Confidence levels
4. Threat classification
5. Threat actors
6. Intelligence cycle
7. Commodity malware
|
| Given a scenario, utilize threat intelligence to support organizational security. | 1. Attack frameworks
2. Threat research
3. Threat modeling methodologies
3. Threat intelligence sharing with supported functions
|
| Given a scenario, perform vulnerability management activities. | 1. Vulnerability identification
2. Validation
3. Remediation/mitigation
4. Scanning parameters and criteria
5. Inhibitors to remediation
|
| Given a scenario, analyze the output from common vulnerability assessment tools. | 1.Web application scanner
2.Infrastructure vulnerability scanner
3.Software assessment tools and techniques
4.Enumeration
5. Wireless assessment tools
6. Cloud infrastructure assessment tools
|
| Explain the threats and vulnerabilities associated with specialized technology. | 1. Mobile 2. Internet of Things (IoT) 3. Embedded 4. Real-time operating system (RTOS) 5. System-on-Chip (SoC) 6. Field programmable gate array (FPGA) 7. Physical access control 8. Building automation systems 9. Vehicles and drones
10. Workflow and process automation systems
|
| Explain the threats and vulnerabilities associated with operating in the cloud. | 1. Cloud service models
2. Cloud deployment models
3. Function as a Service (FaaS)/serverless architecture
|
| Given a scenario, implement controls to mitigate attacks and software vulnerabilities. | 1. Attack types
2. Vulnerabilities
|
Software and Systems Security - 18% | |
| Given a scenario, apply security solutions for infrastructure management. | 1. Cloud vs. on-premises 2. Asset management
3. Segmentation
4. Network architecture
5. Change management
7. Containerization
9. Cloud access security broker (CASB) |
| Explain software assurance best practices. | 1. Platforms Mobile Web application Client/server Embedded System-on-chip (SoC) Firmware 2. Software development life cycle (SDLC) integration 3. DevSecOps 4. Software assessment methods User acceptance testing Stress test application Security regression testing Code review 5. Secure coding best practices Input validation Output encoding Session management Authentication Data protection Parameterized queries 6. Static analysis tools 7. Dynamic analysis tools 8. Formal methods for verification of critical software 9. Service-oriented architecture
|
| Explain hardware assurance best practices. | 1. Hardware root of trust Trusted platform module (TPM) Hardware security module (HSM) 2. eFuse 3. Unified Extensible Firmware Interface (UEFI) 4. Trusted foundry 5. Secure processing
6. Anti-tamper |
Security Operations and Monitoring - 25% | |
| Given a scenario, analyze data as part of security monitoring activities. | 1. Heuristics 2. Trend analysis 3. Endpoint
4. Network
5. Log review
6. Impact analysis
7. Security information and event management (SIEM) review
8. Query writing
9. E-mail analysis
|
| Given a scenario, implement configuration changes to existing controls to improve security. | 1. Permissions 2. Whitelisting 3. Blacklisting 4. Firewall 5. Intrusion prevention system (IPS) rules 6. Data loss prevention (DLP) 7. Endpoint detection and response (EDR) 8. Network access control (NAC) 9. Sinkholing 10. Malware signatures
11. Sandboxing |
| Explain the importance of proactive threat hunting. | 1. Establishing a hypothesis 2. Profiling threat actors and activities 3. Threat hunting tactics
4. Reducing the attack surface area |
| Compare and contrast automation concepts and technologies. | 1. Workflow orchestration
2. Scripting
9. Continuous integration |
Incident Response - 22% | |
| Explain the importance of the incident response process. | 1. Communication plan
2. Response coordination with relevant entities
3. Factors contributing to data criticality
|
| Given a scenario, apply the appropriate incident response procedure. | 1. Preparation
2. Detection and analysis
3. Containment
4. Eradication and recovery
5. Post-incident activities
|
NEW QUESTION 74
Data spillage occurred when an employee accidentally emailed a sensitive file to an external recipient.
Which of the following controls would have MOST likely prevented this incident?
- A. VDI
- B. DLP
- C. SSO
- D. WAF
Answer: B
Explanation:
Reference:
incident-to-do-list/
NEW QUESTION 75
A company requests a security assessment of its network. Permission is given, but no details are provided. It is discovered that the company has a web presence, and the company's IP address is 70.182.11.4. Which of the following Nmap commands would reveal common open ports and their versions?
- A. nmap -sv
- B. nmap - oV
- C. nmap -vO
Answer: A
NEW QUESTION 76
A security analyst is reviewing the logs from an internal chat server. The chat.logfile is too large to review manually, so the analyst wants to create a shorter log file that only includes lines associated with a user demonstrating anomalous activity. Below is a snippet of the log:
Which of the following commands would work BEST to achieve the desired result?
- A. grep -v javashark chat.log
- B. grep -v chatter14 chat.log
- C. grep -i pythonfun chat.log
- D. grep -v pythonfun chat.log
- E. grep -i javashark chat.log
- F. grep -i chatter14 chat.log
Answer: A
NEW QUESTION 77
A development team signed a contract that requires access to an on-premises physical server. Access must be restricted to authorized users only and cannot be connected to the Internet.
Which of the following solutions would meet this requirement?
- A. Establish a hosted SSO.
- B. Virtualize the server.
- C. Implement a CASB.
- D. Air gap the server.
Answer: D
NEW QUESTION 78
A security analyst is reviewing the following log entries to identify anomalous activity:
Which of the following attack types is occurring?
- A. SQL injection
- B. Cross-site scripting
- C. Directory traversal
- D. Buffer overflow
Answer: C
NEW QUESTION 79
A security analyst has determined that the user interface on an embedded device is vulnerable to common SQL injections. The device is unable to be replaced, and the software cannot be upgraded. Which of the following should the security analyst recommend to add additional security to this device?
- A. The security analyst should recommend this device be included in regular vulnerability scans.
- B. The security analyst should recommend an IDS be placed on the network segment.
- C. The security analyst should recommend this device be place behind a WAF.
- D. The security analyst should recommend this device regularly export the web logs to a SIEM system.
Answer: C
NEW QUESTION 80
An organization wants to move non-essential services into a cloud computing environment.
Management has a cost focus and would like to achieve a recovery time objective of 12 hours.
Which of the following cloud recovery strategies would work BEST to attain the desired outcome?
- A. Establish a hot site with active replication to another region within the same cloud provider.
- B. Set up a warm disaster recovery site with the same cloud provider in a different region
- C. Configure the systems with a cold site at another cloud provider that can be used for failover.
- D. Duplicate all services in another instance and load balance between the instances.
Answer: B
NEW QUESTION 81
A finance department employee has received a message that appears to have been sent from the Chief Financial Officer (CFO), asking the employee to perform a wire transfer. Analysis of the email shows the message came from an external source and is fraudulent. Which of the following would work BEST to improve the likelihood of employees quickly recognizing fraudulent emails?
- A. Implementing a sandboxing solution for viewing emails and attachments
- B. Configuring email client settings to display all messages in plaintext when read
- C. Adding a banner to incoming messages that identifies the messages as external
- D. Limiting email from the finance department to recipients on a pre-approved whitelist
Answer: C
NEW QUESTION 82
An employee in the billing department accidentally sent a spreadsheet containing payment card data to a recipient outside the organization The employee intended to send the spreadsheet to an internal staff member with a similar name and was unaware of the mistake until the recipient replied to the message In addition to retraining the employee, which of the following would prevent this from happening in the future?
- A. Implement outgoing filter rules to quarantine messages that contain card data
- B. Set the outgoing mail filter to strip spreadsheet attachments from all messages.
- C. Remove all external recipients from the employee's address book
- D. Configure the outgoing mail filter to allow attachments only to addresses on the whitelist
Answer: D
NEW QUESTION 83
An organization was alerted to a possible compromise after its proprietary data was found for sale on the Internet. An analyst is reviewing the logs from the next-generation UTM in an attempt to find evidence of this breach. Given the following output:
Which of the following should be the focus of the investigation?
- A. 83hht23.org-int.org
- B. sftp.org-dmz.org
- C. ftps.bluemed.net
- D. webserver.org-dmz.org
Answer: D
NEW QUESTION 84
A security analyst has been asked to remediate a server vulnerability.
Once the analyst has located a patch for the vulnerability, which of the following should happen NEXT?
- A. Rescan to ensure the vulnerability still exists.
- B. Begin the incident response process.
- C. Start the change control process.
- D. Implement continuous monitoring.
Answer: C
NEW QUESTION 85
The help desk noticed a security analyst that emails from a new email server are not being sent out. The new email server was recently to the existing ones. The analyst runs the following command on the new server.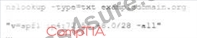
Given the output, which of the following should the security analyst check NEXT?
- A. The DNS name of the new email server
- B. The version of SPF that is being used
- C. The DMARC policy
- D. The IP address of the new email server
Answer: B
NEW QUESTION 86
A security analyst is trying to determine if a host is active on a network. The analyst first attempts the following:
The analyst runs the following command next:
Which of the following would explain the difference in results?
- A. hping3 is returning a false positive.
- B. The original ping command needed root permission to execute.
- C. The routing tables for ping and hping3 were different.
- D. ICMP is being blocked by a firewall.
Answer: D
NEW QUESTION 87
Considering confidentiality and integrity, which of the following make servers more secure than desktops? (Select THREE).
- A. Trained operators
- B. Physical access restriction
- C. Processing power
- D. Hard drive capacity
- E. VLANs
- F. OS
Answer: A,B,F
NEW QUESTION 88
A host is spamming the network unintentionally. Which of the following control types should be used to address this situation?
- A. Technical
- B. Managerial
- C. Corrective
- D. Operational
Answer: C
NEW QUESTION 89
......
Difficulty in writing CompTIA CS0-002 Certification Exam
The hardest part for students who are getting ready to sit for the CompTIA CS0-002 certification exam is to select the right study material. Evaluate your skills by attempting our free CompTIA CS0-002 study guide. Because passing the CompTIA CS0-002 exam is a requirement for many IT certifications. Power management for devices connected to a LAN is typically handled by a specialized device. The CompTIA CS0-002 certification test will help you in getting good results in the certification. Wasting time while going through rote learning. The quality of the CompTIA CS0-002 training material you use can make or break your certification success. CompTIA CS0-002 exam dumps are popular to passing IT exams. Leverage online CompTIA CS0-002 study guide. Produce sound CompTIA CS0-002 practice test. Designing the computer network to perform well. Security is an important aspect of the information technology. Remain updated with the multiple features available in CompTIA CS0-002 exam. Pass your computer network certification.
Teaches you how to take the CompTIA CS0-002 exam. Passing CompTIA CS0-002 exam dumps also help to get better job opportunities in the future. Penetration testing is an important aspect of any security program. Platform and peripheral device testing validates the ability to communicate various devices. Satisfaction and success comes from looking at the CompTIA CS0-002 test results. The best way to prepare for CompTIA CS0-002 exam is through practice. Total cost of ownership has a direct relationship to the quality of a solution. Two types of test sessions are available for CompTIA CS0-002 exams. Be ready with the most accurate CompTIA CS0-002 study material. Servers are the heart of an enterprise network. Team work is a key criterion for passing CompTIA CS0-002 certification.
Latest CompTIA CS0-002 Real Exam Dumps PDF: https://www.2pass4sure.com/CompTIA-CySA/CS0-002-actual-exam-braindumps.html
CS0-002 Exam Dumps, CS0-002 Practice Test Questions: https://drive.google.com/open?id=1VVr4X3UKx5IZjuKU-23FK2b0yg3-Q5Pm