

New 2021 Guaranteed Success with 2Pass4sure CAS-003 Dumps CompTIA PDF Questions
Exceptional Practice To CompTIA Advanced Security Practitioner (CASP) Pass the First Time
About Exam
CAS-003 exam consists of a maximum of 90 questions that need to be completed in 165 minutes. The questions are in multiple-choice and performance-based format. You have the option to choose between two languages — English and Japanese. There is no scaled score in this exam; you either pass or fail. CAS-003 will cost $452 for candidates from the USA.
After the successful completion of the test, the candidates will be granted the CASP+ certification that will be valuable for both the employee and the enterprise. This certificate has been approved by the United States Department of Defense and its holders are preferred by Dell and HP for their advanced security personnel.
NEW QUESTION 278
Immediately following the report of a potential breach, a security engineer creates a forensic image of the server in question as part of the organization incident response procedure. Which of the must occur to ensure the integrity of the image?
- A. A hash value of the image must be computed.
- B. A duplicate copy of the image must be maintained
- C. The disk containing the image must be placed in a seated container.
- D. The image must be password protected against changes.
Answer: A
NEW QUESTION 279
A security engineer is investigating a compromise that occurred between two internal computers.
The engineer has determined during the investigation that one computer infected another. While reviewing the IDS logs, the engineer can view the outbound callback traffic, but sees no traffic between the two computers. Which of the following would BEST address the IDS visibility gap?
- A. Install network taps at the edge of the network.
- B. Send syslog from the IDS into the SIEM.
- C. Install HIDS on each computer.
- D. SPAN traffic form the network core into the IDS.
Answer: C
Explanation:
SPANNING traffic from the core to the IDS is going to dump a whole lot of traffic back to your IDS unnecessarily and dump duplicate communications toward the IDS and tax your bandwidth. The threat is already inside. computer to computer communication on the same subnet may or may not go back through the core. HIDS is the sensible, logical solution.
NEW QUESTION 280
A user has a laptop configured with multiple operating system installations. The operating systems are all installed on a single SSD, but each has its own partition and logical volume. Which of the following is the BEST way to ensure confidentiality of individual operating system data?
- A. Encryption of each individual partition
- B. FDE of the entire SSD as a single disk
- C. FDE of each logical volume on the SSD
- D. Encryption of the SSD at the file level
Answer: A
Explanation:
In this question, we have multiple operating system installations on a single disk. Some operating systems store their boot loader in the MBR of the disk. However, some operating systems install their boot loader outside the MBR especially when multiple operating systems are installed. We need to encrypt as much data as possible but we cannot encrypt the boot loaders. This would prevent the operating systems from loading.
Therefore, the solution is to encrypt each individual partition separately.
Incorrect Answers:
B: The question is asking for the BEST way to ensure confidentiality of individual operating system data. Individual file encryption could work but if files are ever added to the operating systems (for updates etc.), you would have to manually encrypt the new files as well. A better solution would be to encrypt the entire partition. That way any new files added to the operating system would be automatically encrypted.
C: You cannot perform full disk encryption on an individual volume. Full disk encryption encrypts the entire disk.
D: FDE of the entire SSD as a single disk would encrypt the boot loaders which would prevent the operating systems from booting.
NEW QUESTION 281
An administrator believes that the web servers are being flooded with excessive traffic from time to time. The administrator suspects that these traffic floods correspond to when a competitor makes major announcements. Which of the following should the administrator do to prove this theory?
- A. Implement a honey pot to capture traffic during the next attack.
- B. Configure the servers for high availability to handle the additional bandwidth.
- C. Implement data analytics to try and correlate the occurrence times.
- D. Log all traffic coming from the competitor's public IP addresses.
Answer: C
Explanation:
There is a time aspect to the traffic flood and if you correlate the data analytics with the times that the incidents happened, you will be able to prove the theory.
Incorrect Answers:
B: A honey pot is designed to attract traffic and this will not prove the theory.
C: Configuring any of your servers for high availability will only accommodate the competitor and not prove your theory.
D: Logging all incoming traffic will not prove the theory as you want to check whether the incidents occur when the competitor makes major announcement a not all of the incoming traffic, even it if is from the competitor.
References:
Gregg, Michael, and Billy Haines, CASP CompTIA Advanced Security Practitioner Study Guide, John Wiley & Sons, Indianapolis, 2012, pp. 114-115
NEW QUESTION 282
An organization is in the process of integrating its operational technology and information technology areas. As part of the integration, some of the cultural aspects it would like to see include more efficient use of resources during change windows, better protection of critical infrastructure, and the ability to respond to incidents. The following observations have been identified:
* The ICS supplier has specified that any software installed will result in lack of support.
* There is no documented trust boundary defined between the SCADA and corporate networks.
* Operational technology staff have to manage the SCADA equipment via the engineering workstation.
* There is a lack of understanding of what is within the SCADA network.
Which of the following capabilities would BEST improve the security position?
- A. VNC, router, and HIPS
- B. Proxy, VPN, and WAF
- C. IDS, NAC, and log monitoring
- D. SIEM, VPN, and firewall
Answer: D
NEW QUESTION 283
A security administrator must configure the database server shown below to comply with the four requirements listed. Drag and drop the appropriate ACL that should be configured on the database server to its corresponding requirement. Answer options may be used once or not at all.
Answer:
Explanation: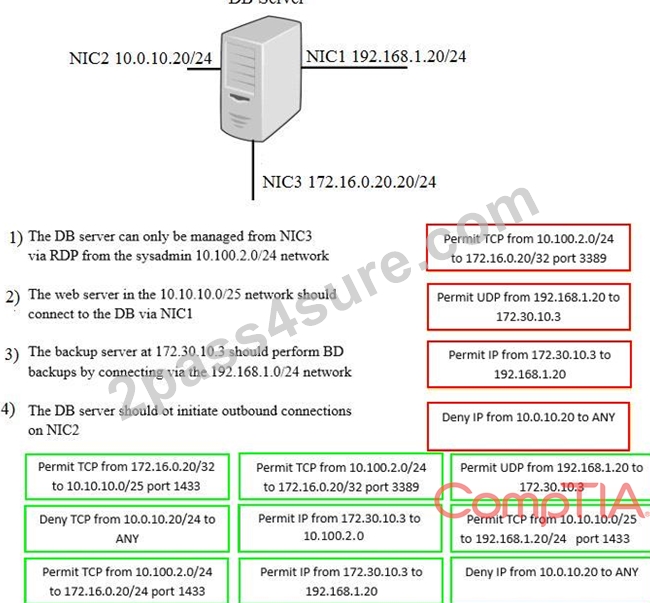
NEW QUESTION 284
A security analyst for a bank received an anonymous tip on the external banking website showing the following:
Protocols supported
TLS 1.0
SSL 3
SSL 2
Cipher suites supported
TLS_ECDHE_RSA_WITH_AES_256_CBC_SHA-ECDH p256r1
TLS_DHE_RSA_WITH_AES_256_CBC_SHA-DH 1024bit
TLS_RSA_WITH_RC4_128_SHA
TLS_FALLBACK_SCSV non supported
POODLE
Weak PFS
OCSP stapling supported
Which of the following should the analyst use to reproduce these findings comprehensively?
- A. Perform a POODLE (SSLv3) attack using an exploitations framework and inspect the output.
- B. Review CA-supported ciphers and inspect the connection through an HTTP proxy.
- C. Query the OCSP responder and review revocation information for the user certificates.
- D. Inspect the server certificate and simulate SSL/TLS handshakes for enumeration.
Answer: B
NEW QUESTION 285
A security policy states that all applications on the network must have a password length of eight characters. There are three legacy applications on the network that cannot meet this policy. One system will be upgraded in six months, and two are not expected to be upgraded or removed from the network. Which of the following processes should be followed?
- A. Establish a risk matrix
- B. Provide a business justification to avoid the risk
- C. Provide a business justification for a risk exception
- D. Inherit the risk for six months
Answer: C
Explanation:
The Exception Request must include:
A description of the non-compliance.
The anticipated length of non-compliance (2-year maximum).
The proposed assessment of risk associated with non-compliance.
The proposed plan for managing the risk associated with non-compliance.
The proposed metrics for evaluating the success of risk management (if risk is significant).
The proposed review date to evaluate progress toward compliance.
An endorsement of the request by the appropriate Information Trustee (VP or Dean).
Incorrect Answers:
A: A risk matrix can be used to determine an overall risk ranking before determining how the risk will be dealt with.
B: Inheriting the risk for six months means that it has been decided the benefits of moving forward outweighs the risk.
C: Avoiding the risk is not recommended as the applications are still being used.
References:
http://www.rit.edu/security/sites/rit.edu.security/files/exception%20process.pdf Gregg, Michael, and Billy Haines, CASP CompTIA Advanced Security Practitioner Study Guide, John Wiley & Sons, Indianapolis, 2012, p. 218
NEW QUESTION 286
A large company is preparing to merge with a smaller company. The smaller company has been very profitable, but the smaller company's main applications were created in-house. Which of the following actions should the large company's security administrator take in preparation for the merger?
- A. An ROI calculation should be performed to determine which company's application should be used.
- B. A review of the mitigations implemented from the most recent audit findings of the smaller company should be performed.
- C. A security assessment should be performed to establish the risks of integration or co-existence.
- D. A regression test should be performed on the in-house software to determine security risks associated with the software.
Answer: C
Explanation:
Explanation
With any merger regardless of the monetary benefit there is always security risks and prior to the merger the security administrator should assess the security risks to as to mitigate these.
NEW QUESTION 287
The Chief Information Security Officer (CISO) at a company knows that many users store business documents on public cloud-based storage, and realizes this is a risk to the company. In response, the CISO implements a mandatory training course in which all employees are instructed on the proper use of cloud-based storage. Which of the following risk strategies did the CISO implement?
- A. Accept
- B. Avoid
- C. Mitigate
- D. Transfer
Answer: C
Explanation:
Mitigation means that a control is used to reduce the risk. In this case, the control is training.
Incorrect Answers:
A: To avoid could mean not performing an activity that might bear risk.
B: To accept the risk means that the benefits of moving forward outweigh the risk.
D: To transfer the risk means that the risk is deflected to a third party.
References:
Gregg, Michael, and Billy Haines, CASP CompTIA Advanced Security Practitioner Study Guide, John Wiley & Sons, Indianapolis, 2012, pp. 88, 218
https://en.wikipedia.org/wiki/Risk_management
NEW QUESTION 288
A security architect is determining the best solution for a new project. The project is developing a new
intranet with advanced authentication capabilities, SSO for users, and automated provisioning to
streamline Day 1 access to systems. The security architect has identified the following requirements:
1. Information should be sourced from the trusted master data source.
2. There must be future requirements for identity proofing of devices and users.
3. A generic identity connector that can be reused must be developed.
4. The current project scope is for internally hosted applications only.
Which of the following solution building blocks should the security architect use to BEST meet the
requirements?
- A. NAC, radius, 802.1x, centralized active directory
- B. SAML, context-aware authentication, oAuth, WAYF
- C. LDAP, multifactor authentication, oAuth, XACML
- D. AD, certificate-based authentication, Kerberos, SPML
Answer: C
NEW QUESTION 289
A company's IT department currently performs traditional patching, and the servers have a significant longevity that may span over five years. A security architect is moving the company toward an immune server architecture in which servers are replaced rather than patched. Instead of having static servers for development, test, and production, the severs will move from environment to environment dynamically.
Which of the following are required to move to this type of architecture? (Select Two.)
- A. Load balancers
- B. Forward proxy
- C. Network segmentation
- D. Automated deployments
- E. Netflow
Answer: A,B
NEW QUESTION 290
A red team is able to connect a laptop with penetration testing tools directly into an open network port The team then is able to take advantage of a vulnerability on the domain controller to create and promote a new enterprise administrator. Which of the following technologies would MOST likely eliminate this attack vector m the future?
- A. Monitor for anomalous creations of privileged domain accounts
- B. Ensure the domain controller has the latest security patches
- C. Install a NIPS with rules appropriate to drop most exploit traffic
- D. Implement 802.1X with certificate-based authentication
Answer: B
NEW QUESTION 291
At a meeting, the systems administrator states the security controls a company wishes to implement seem
excessive, since all of the information on the company's web servers can be obtained publicly and is not
proprietary in any way. The next day the company's website is defaced as part of an SQL injection attack,
and the company receives press inquiries about the message the attackers displayed on the website.
Which of the following is the FIRST action the company should take?
- A. Call a press conference to explain that the company has been hacked.
- B. Refer to and follow procedures from the company's incident response plan.
- C. Establish chain of custody for all systems to which the systems administrator has access.
- D. Conduct a detailed forensic analysis of the compromised system.
- E. Inform the communications and marketing department of the attack details.
Answer: B
NEW QUESTION 292
A recent assessment identified that several users' mobile devices are running outdated versions of endpoint security software that do not meet the company's security policy. Which of the following should be performed to ensure the users can access the network and meet the company's security requirements?
- A. Vulnerability assessment
- B. Device quarantine
- C. Risk assessment
- D. Incident management
- E. Patch management
Answer: E
NEW QUESTION 293
Company ABC's SAN is nearing capacity, and will cause costly downtimes if servers run out disk space. Which of the following is a more cost effective alternative to buying a new SAN?
- A. Enable multipath to increase availability
- B. Enable deduplication on the storage pools
- C. Implement snapshots to reduce virtual disk size
- D. Implement replication to offsite datacenter
Answer: B
Explanation:
Storage-based data deduplication reduces the amount of storage needed for a given set of files.
It is most effective in applications where many copies of very similar or even identical data are stored on a single disk.
It is common for multiple copies of files to exist on a SAN. By eliminating (deduplicating) repeated copies of the files, we can reduce the disk space used on the existing SAN. This solution is a cost effective alternative to buying a new SAN.
NEW QUESTION 294
An organization is currently performing a market scan for managed security services and EDR capability. Which of the following business documents should be released to the prospective vendors in the first step of the process? (Select TWO).
- A. NDA
- B. MOU
- C. RFQ
- D. MSA
- E. RFI
- F. RFP
Answer: A,E
NEW QUESTION 295
A completely new class of web-based vulnerabilities has been discovered. Claims have been made that all common web-based development frameworks are susceptible to attack. Proof-of- concept details have emerged on the Internet. A security advisor within a company has been asked to provide recommendations on how to respond quickly to these vulnerabilities. Which of the following BEST describes how the security advisor should respond?
- A. Review vulnerability write-ups posted on the Internet. Respond to management with a recommendation to wait until the news has been independently verified by software vendors providing the web application software.
- B. Hire an independent security consulting agency to perform a penetration test of the web servers.
Advise management of any `high' or `critical' penetration test findings and put forward recommendations for mitigation. - C. Assess the reliability of the information source, likelihood of exploitability, and impact to hosted data. Attempt to exploit via the proof-of-concept code. Consider remediation options.
- D. Notify all customers about the threat to their hosted data. Bring the web servers down into
"maintenance mode" until the vulnerability can be reliably mitigated through a vendor patch.
Answer: C
Explanation:
The first thing you should do is verify the reliability of the claims. From there you can assess the likelihood of the vulnerability affecting your systems. If it is determined that your systems are likely to be affected by the exploit, you need to determine what impact an attack will have on your hosted data. Now that you know what the impact will be, you can test the exploit by using the proof-of-concept code. That should help you determine your options for dealing with the threat (remediation).
NEW QUESTION 296
A project manager is working with a team that is tasked to develop software applications in a structured
environment and host them in a vendor's cloud-based infrastructure. The organization will maintain
responsibility for the software but will not manage the underlying server applications. Which of the following
does the organization plan to leverage?
- A. Network virtualization
- B. IaaS
- C. PaaS
- D. SaaS
- E. Hybrid cloud
Answer: C
NEW QUESTION 297
A security engineer is embedded with a development team to ensure security is built into products being
developed. The security engineer wants to ensure developers are not blocked by a large number of
security requirements applied at specific schedule points.
Which of the following solutions BEST meets the engineer's goal?
- A. Enforce code quality and reuse standards into the requirements definition phase of the waterfall
development process. - B. Develop and implement a set of automated security tests to be installed on each development team
leader's workstation. - C. Deploy an integrated software tool that builds and tests each portion of code committed by developers
and provides feedback. - D. Schedule weekly reviews of al unit test results with the entire development team and follow up between
meetings with surprise code inspections.
Answer: A
NEW QUESTION 298
A security incident responder discovers an attacker has gained access to a network and has overwritten key system files with backdoor software. The server was reimaged and patched offline.
Which of the following tools should be implemented to detect similar attacks?
- A. TPM
- B. Vulnerability scanner
- C. Host-based firewall
- D. NIPS
- E. File integrity monitor
Answer: C
NEW QUESTION 299
Which of the following attacks can be mitigated by proper data retention policies?
- A. Man-in-the browser
- B. Dumpster diving
- C. Watering hole
- D. Spear phishing
Answer: B
NEW QUESTION 300
An administrator has noticed mobile devices from an adjacent company on the corporate wireless network.
Malicious activity is being reported from those devices. To add another layer of security in an enterprise environment, an administrator wants to add contextual authentication to allow users to access enterprise resources only while present in corporate buildings. Which of the following technologies would accomplish this?
- A. Port security
- B. GPS
- C. Rogue device detection
- D. Bluetooth
Answer: B
NEW QUESTION 301
......
Career Opportunities
The job titles that the candidates who pass the CompTIA CAS-003 exam can take up include a Security Engineer, an Application Security Engineer, a Technical Lead Analyst, and a Security Architect, among others. The salary potential for these professionals is an average of $105,000 per annum. Depending on their level of experience, this figure may be even higher.
CAS-003 EXAM DUMPS WITH GUARANTEED SUCCESS: https://www.2pass4sure.com/CASP-Recertification/CAS-003-actual-exam-braindumps.html